 Reliable data
Collect IPDR & Logs
High-frequency streaming ingest from routers, BNGs, and firewalls.
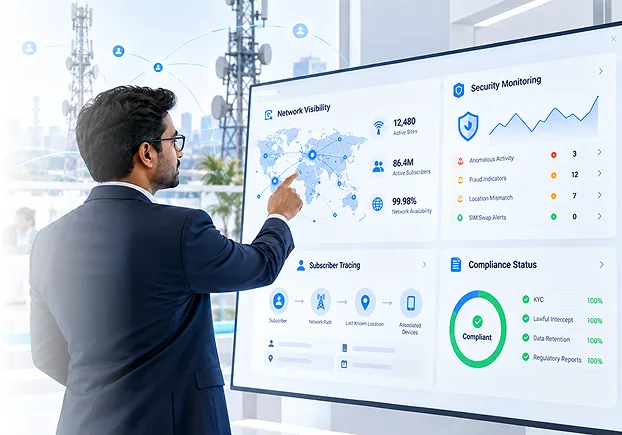
IconTrace helps ISPs and telecom operators collect IPDR data, analyze network activity, detect threats, investigate incidents and stay audit-ready from one intelligent platform.

Real-Time Intelligence
Sub-second telemetry metrics

Multi-Source IPDR
BNG, CGNAT, AAA & NetFlow

Audit-Ready Logs
Lawful interception and LEA ready

24×7 Active Monitoring
Automated anomaly detection
HOW ICONTRACE WORKS
From wireline packets to certified court-ready electronic evidence in 8 orchestrated stages.
Reliable dataHigh-frequency streaming ingest from routers, BNGs, and firewalls.
 Better context
Align IP translation sessions with RADIUS, TACACS+, and DHCP leases.
 Deep visibility
Protocol identification, bandwidth quotas, and DPI traffic inspection.
 Early detection
Detect port scans, botnet command loops, and DDoS amplification.
 Faster triage
Instant timeline forensics linking public IP, time slot, and subscriber ID.
 Rapid response
Push alerts to NOC monitors, SIEM clusters, and law enforcement portals.
 Audit ready
Statutory compression vault ensuring immutability for regulatory audits.
 Continuous QoS
Optimize peering capacity, cache routing, and network investments.
CORE CAPABILITIES
Modular, carrier-grade architectural blocks engineered to handle tens of gigabits of uninterrupted signaling.


Choose a challenge and see how IconTrace transforms the operational workflow.
Challenge solved
Turn disconnected data into a clear investigation journey.

IPDR Event
Dest Port: 445Proto: TCP / RST
Raw log captured

Session Correlation
CGNAT translationPublic → Private IP
Radius matched

Subscriber Mapping
User: SUB-44091IMSI / MAC bound
Identity confirmed

Evidence Timeline
Events, sessions,firewall logs
Full context

Investigation Result
Actionable dossiercreated
Complete Trace • 0.4s
Relevant network, subscriber and session context connected automatically.
ONE PLATFORM. COMPLETE NETWORK INTELLIGENCE.
Collect, analyze, investigate and act without switching between disconnected systems.
 Ingestion
Capture high-volume network records across multi-vendor environments with sub-millisecond precision.
Explore feature: High-Performance IPDR Capture Analytics
Understand subscribers, applications, traffic surges and bandwidth utilization instantly.
Explore feature: Real-Time Analytics Security
Detect anomalous threats, botnet communications, policy violations and suspicious external activity.
Explore feature: Security Intelligence Legal
Stay audit-ready with strict statutory retention, tamper-proof logs, and lawful interception support.
Explore feature: Compliance & Regulatory Operations
Monitor subscriber bandwidth thresholds, FUP quota breaches, and protocol allocation metrics.
Explore feature: Usage Management Storage
Manage petabyte-scale IPDR data with multi-tier storage, column-oriented indexing, and 90% compression.
Explore feature: Data Management Alerts
Respond faster through configurable real-time alert triggers, webhook dispatches, and NOC escalation paths.
Explore feature: Alerts & Notifications Ecosystem
Seamlessly connect IconTrace with your OSS/BSS, SIEM, SOAR, AAA servers, and existing billing platforms.
Explore feature: Open APIs & IntegrationsTIERED DATA ENGINE
Petabyte-scale IPDR data requires balanced storage engineering. IconTrace dynamically tiers records across memory, low-latency NVMe arrays, and encrypted compressed vaults.

Automated data lifecycle management migrating cold data seamlessly.

Proprietary columnar compression delivers up to 10:1 space reductions.

Adhere to 1-year, 2-year, or indefinite telecommunication compliance laws.

Retrieve historical IPDR records across months in seconds, not hours.

Real-time NetFlow, IPFIX, RADIUS, CGNAT stream

Sub-second query response • 0 to 7 days

High-density indexed columns • 8 to 90 days

Tamper-evident, WORM-compliant • 1 to 5 years
OPEN ECOSYSTEM
Zero vendor lock-in. Connect seamlessly across core, edge, access, and enterprise IT management stacks.
DEFENSE & SURVEILLANCE
Automated threat detection tailored for telecom scale with deep subscriber session traceability.

Real-time alerts for volumetric UDP/ICMP floods and reflection attempts.

Isolate infected subscriber hosts probing external subnets.

Identify C2 server connections and recursive DNS tunneling.

Detect unauthorized peer-to-peer tunnels or proxy abuse.

Algorithmic baseline spikes against normal regional usage profiles.

Cross-check live traffic against global threat intelligence feeds.
Event signature
High-Frequency TCP SYN Scanning
Recommended workflow action
REGULATORY ASSURANCE
IconTrace supports regulatory compliance workflows with certified audit trails, automated retention policies, and cryptographically verified data integrity.
Multi-interface feed
WORM statutory storage
Sub-second timeline
Immutable change logs
LEA certified export

Provides ETSI TS 102 232 and 3GPP compliant interfaces enabling telecom operators to fulfill lawful warrant handovers safely.

Every user query, export, and record view is tracked with cryptographic hashing to guarantee non-repudiation in court evidence.

Engineered with strict role-based access control (RBAC), subscriber privacy masking, and automated statutory data destruction.
DEPLOYMENT OPTIONS
Deploy where your network data lives with zero compromise on throughput or security.

AWS, Azure, and Google Cloud turnkey deployment with automated autoscaling ingestion pools.
Managed SaaS

OpenStack, VMware vSphere, or Kubernetes clusters within sovereign telecom cloud perimeters.
Isolated VPC

Direct deployment on operator-owned rack hardware for maximum packet processing throughput.
Air-Gapped Capable

Active-active multi-datacenter clustering with sub-second failover and cross-site synchronization.
99.999% SLA
THE ICONTRACE ADVANTAGE
Built from the ground up for high-assurance telecom intelligence.

Eliminates blind spots between access, core, and peering links with complete wire-speed collection.

Translates cryptic network packets into immediate actionable subscriber threat remediation.

Reduces multi-day manual investigation forensic cycles into instant sub-second lookups.

Guarantees peace of mind during national telecom regulatory inspections and lawful audits.
READY TO SEE ICONTRACE IN YOUR NETWORK?
Schedule a technical session with our telecom intelligence specialists to explore live IPDR capture, session correlation, and investigation pipelines.
What you will experience in the demo:
FREQUENTLY ASKED QUESTIONS
Common queries from telecom network architects, CTOs, and compliance directors.
IconTrace utilizes distributed micro-probes and zero-copy DPDK/eBPF ingestion kernels capable of processing millions of flows per second directly off core BNG, CGNAT, and NetFlow exporters with minimal compute overhead.
Yes. By ingesting both CGNAT translation mapping tables and RADIUS accounting streams in real-time, IconTrace correlates external public port-allocated sessions to exact subscriber IMSIs, MACs, or user IDs within fractions of a second.
IconTrace is vendor-neutral. It unifies Cisco, Juniper, Huawei, Nokia, and MikroTik BNG interfaces and works with BNG/BRAS, CGNAT, RADIUS/TACACS+ and DHCP servers, routers, switches, and next-generation firewalls, ingesting NetFlow, IPFIX, RADIUS, and CGNAT streams. OSS/BSS, SIEM/SOAR, and REST/Kafka APIs connect it to the rest of your stack.
It complies with ETSI TS 102 232 and national security standards by offering role-restricted interfaces, cryptographically sealed export bundles, and tamper-evident audit logs that ensure chain-of-custody validity for legal proceedings.
With proprietary columnar compression (yielding up to 90% disk space reduction), operators can store 1 to 5+ years of complete IPDR records while maintaining automated lifecycle migration into cost-effective cold object storage.
Yes. IconTrace provides rich REST APIs, Kafka event buses, and Syslog forwarders that stream enriched anomaly events directly into Splunk, IBM QRadar, Microsoft Sentinel, and custom Grafana NOC dashboards.
We support 100% on-premise bare-metal deployments inside sovereign operator data centers, fully air-gapped installations, private cloud (OpenStack/Kubernetes), and managed hybrid configurations.